Cloudflare Announces Protection Measures Against Critical PHP Vulnerabilities
Are Millions of Websites at Risk?
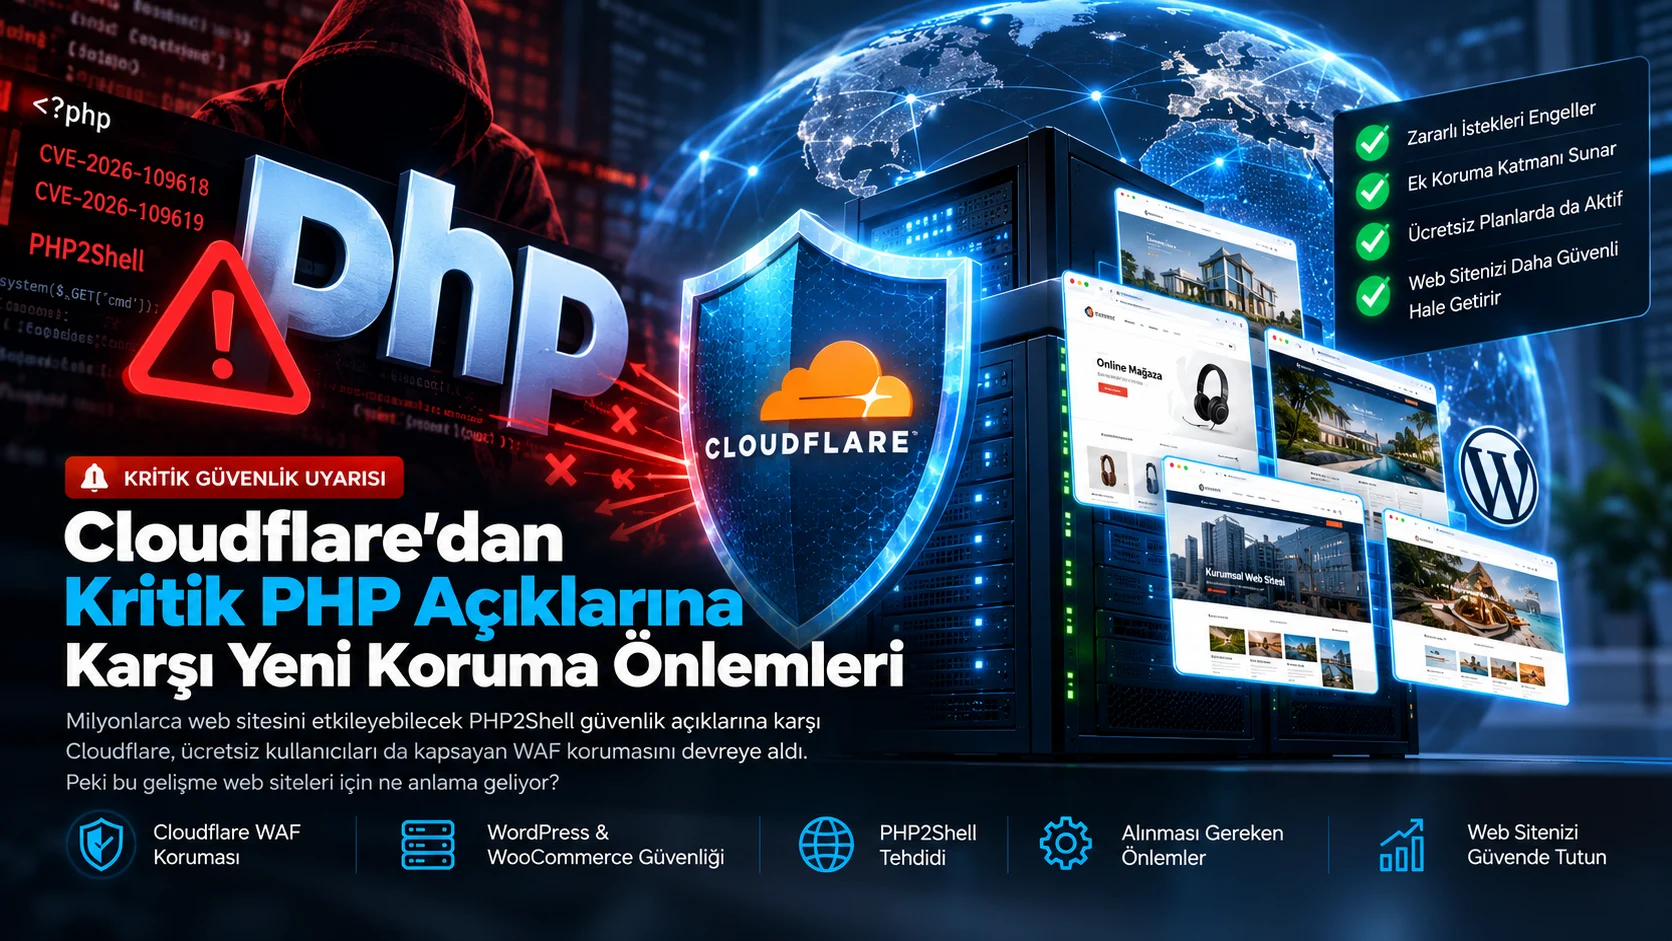
Critical security vulnerabilities that emerged in the PHP infrastructure on October 21, 2026 mobilized website owners and server administrators around the world. Cloudflare has introduced new protection against these vulnerabilities, called PHP2Shell, covering free users.
Critical security vulnerabilities that emerged in the PHP infrastructure on October 21, 2026 mobilized website owners and server administrators around the world. Cloudflare has implemented new protection measures, including free users, against these vulnerabilities called PHP2Shell. So what does this development mean for websites, WordPress users and e-commerce businesses?
Worldwide PHP Security Alert
PHP, one of the most widely used programming languages in the internet world, came to the center of the technology agenda with serious security vulnerabilities that emerged in October 2026.
Two critical vulnerabilities, named PHP2Shell and disclosed to the public on October 21, 2026, can allow attackers to perform unauthorized operations on servers using PHP under certain conditions.
This development concerns not only software developers but also millions of businesses with PHP-based websites.
Because WordPress, WooCommerce, Magento and many special software infrastructures benefit from PHP technology.
The vulnerabilities discovered by security researchers are located directly in the working mechanism of PHP. So the problem is not just limited to an outdated WordPress plugin or an unupdated theme.
The fact that one of the basic software components used by millions of websites around the world is affected once again reveals the importance of security measures.
What is PHP2Shell? Why Is It So Important?
PHP2Shell is the name used to describe two critical vulnerabilities related to PHP's memory management.
These vulnerabilities are tracked with the following security logs:
CVE-2026-109618: Vulnerability in which PHP may use memory data that has not yet been properly prepared under certain error conditions.
CVE-2026-109619: Vulnerability in which PHP can re-access freed memory areas.
Both vulnerabilities pose risks that, under certain circumstances, could cause server processes to crash, expose sensitive information, or remotely execute malicious code.
To put it more simply:
Normally, a website processes the request sent by the visitor and displays the relevant page. However, attackers may try to abuse the way the server performs these operations with specially crafted requests.
As a result of a successful attack, the website may stop working, some information held on the server may be disclosed, or unauthorized operations may be performed on the system.
Therefore, PHP2Shell is considered a much more serious security threat than an ordinary software bug.
Cloudflare Takes Action: Free Users Also Included in the Scope of Protection
Cloudflare, one of the world's leading internet security and performance companies, announced the protection mechanisms it developed against PHP2Shell vulnerabilities to the public on October 21, 2026.
According to Cloudflare's statement, security teams started working on protection rules before the vulnerabilities were announced to the public.
The company said it rolled out new security rules as of 03:02 UTC on October 21, 2026, and that these measures were put into effect approximately nine hours before the public announcement.
One of the key developments here is that protections are not only available to paid Cloudflare subscribers.
Cloudflare has automatically implemented WAF security rules that include free plan users.
Thus, websites using Cloudflare's relevant firewall have an additional layer of defense against known PHP2Shell attack methods.
However, the extent of this protection depends on the Cloudflare configuration used and whether the relevant security rules are active.
What is Cloudflare WAF? How to Protect Websites?
WAF is the abbreviation of the English phrase Web Application Firewall. It is called Web Application Firewall in Turkish.
WAF systems examine HTTP requests from visitors to websites, trying to detect suspicious or potentially harmful types of traffic.
When you visit a website, various data is exchanged between your browser and the web server.
Services like Cloudflare can create a layer of security in front of this traffic when configured correctly.
For example, malicious requests sent by attackers to exploit known vulnerabilities can be blocked if they match relevant security rules.
Key benefits of this system include:
Automatic filtering against known attack methods.
Detecting suspicious HTTP requests.
Blocking certain types of malicious traffic before it reaches the server.
Ability to update security rules against new threats.
Website administrators can track security incidents.
However, WAF systems are not perfect solutions that prevent all cyber attacks.
For effective security, server software must be kept up to date and different layers of protection must be used together.
Cloudflare's New Security Technology: Analyzing Requests and Responses Together
One of the notable innovations in Cloudflare's PHP2Shell security measures is Full Transaction Detection It was a new analysis approach called.
Traditional firewalls often try to detect attacks by examining requests sent to the website.
However, in some attack attempts, simply examining the incoming request may not be enough to understand whether the operation is truly harmful or not.
This new approach developed by Cloudflare can evaluate both the incoming request and the response returned from the server within the scope of the same HTTP transaction.
Thus, the system aims to detect attack attempts more accurately by analyzing the result of a suspicious transaction.
Under certain conditions, server responses that are found to be harmful can also be prevented from being transmitted to the user.
This technology is considered one of the important examples of the transformation of firewalls from systems that only control incoming traffic to solutions that can perform more comprehensive analysis.
Could WordPress and WooCommerce Sites Be Affected?
One of the areas where PHP2Shell vulnerabilities attracted the most attention was the WordPress and WooCommerce infrastructures.
WordPress is a PHP-based content management system used on millions of websites around the world.
WooCommerce is a popular e-commerce solution that runs on WordPress infrastructure and enables businesses to sell online.
Because these systems use PHP, servers running vulnerable PHP versions may be at potential risk.
However, there is an important detail here:
Just because a website uses WordPress or WooCommerce doesn't necessarily mean it's been hacked.
Real risk; It depends on the version of PHP running on the server, security patches, application configuration and protection measures used.
Especially in e-commerce sites, protecting customer information, order records and various system access keys is of great importance.
Therefore, businesses need to regularly check not only WordPress and plugin updates, but also the PHP infrastructure on their servers.
Which Versions Should Be Updated Against PHP Security Vulnerabilities?
The PHP development team released urgent security updates to fix critical vulnerabilities on October 21, 2026.
The versions containing security fixes are:
| PHP version | Version containing security fix |
|---|---|
| PHP 8.2 | 8.2.35 |
| PHP 8.3 | 8.3.36 |
| PHP 8.4 | 8.4.27 |
| PHP 8.5 | 8.5.12 |
These releases include fixes for two critical PHP2Shell vulnerabilities announced on October 21.
The security status of systems using older or out-of-support PHP versions also needs to be evaluated separately.
However, there is another important point.
Related to PHP's session load progress feature on October 23, 2026 CVE-2026-115560 An additional vulnerability has been announced.
According to Cloudflare's updated statement, this additional issue may also affect versions updated for the initial PHP2Shell exploits. The new fix is planned to be released in the next regular PHP release.
Cloudflare states that it also provides protection against known attack attempts against this additional vulnerability. However, systems that change the default session loading progress area name may fall outside the protection scope of the relevant WAF rule.
Therefore, the security process does not end with just applying the first urgent updates.
It is also necessary to monitor new announcements and apply additional security fixes.
Does Using Cloudflare Require PHP Updates?
The answer to this question is definitely no.
The security measures offered by Cloudflare can provide an important layer of protection to prevent attack attempts.
However, it does not completely eliminate a security vulnerability in PHP itself.
While the firewall tries to detect and block malicious requests, the PHP update fixes the security problem within the software.
Therefore, the healthiest approach is to apply both methods together.
Cloudflare firewall provides additional protection. PHP security update aims to fix the basic software vulnerability.
Another important issue is direct server access that does not go through Cloudflare.
If Cloudflare protection can be bypassed through the real IP address of the server, using WAF alone may not be enough.
Therefore, the security approach must cover the DNS, network access, server configuration and application layers together.
What Should Website Owners Do Now?
In the face of PHP2Shell and similar security developments, businesses need to have correct technical controls instead of panicking.
First of all, it is necessary to find out which PHP version the website uses.
Then, it should be checked whether the PHP software on the server has received security updates.
The compatibility status of WordPress, WooCommerce and other software components should be evaluated and necessary updates should be applied in a controlled manner.
The effectiveness of WAF security rules on websites using Cloudflare and any blocking records should be examined.
In addition, basic precautions such as regular backups, server access security and control of system records should not be neglected.
Especially for businesses that process customer information or receive online payments, professional technical infrastructure management is important not only in terms of performance but also data security.
Zeynart Web Bilisim: Strong Infrastructure, Professional Management
Founded in Istanbul in 2014, Zeynart Web Bilişim offers technology solutions to businesses with server management, web hosting and digital infrastructure services, as well as web design and software development activities.
Zeynart Web Bilişim, which manages the technical processes of more than 300 websites today, prioritizes the importance of reliable and sustainable web services.
Solutions such as Germany-based Hetzner server infrastructure, Plesk management panel, Cloudflare technologies and LiteSpeed are among the important components of the technical services offered.
However, a secure web infrastructure cannot be created only by using powerful technologies.
These technologies must be configured correctly, updated and monitored, and measures against possible risks must be evaluated in a timely manner.
Zeynart Web Bilişim considers website management not only as a hosting service but as a long-term technology partnership to protect the digital assets of businesses.
Security developments such as PHP2Shell once again demonstrate the importance of professional server management and up-to-date security practices.
Conclusion: The Security of Your Website Should Not Be Left to Chance
The PHP2Shell vulnerabilities that emerged in October 2026 showed that technologies commonly used in the internet infrastructure may occasionally encounter serious security risks.
Cloudflare's quickly deployed WAF protections have created a significant additional layer of defense for millions of websites.
However, it is still crucial to apply PHP security updates, check server configurations, and follow new security announcements.
The main goal for businesses is not only to seek solutions when a security problem occurs; To create a reliable and sustainable digital infrastructure by evaluating risks in advance.
Zeynart Web Bilişim continues to support businesses to operate safely in the digital world with its experience gained since 2014 and more than 300 websites it manages.
Need professional support on your website's PHP version, server security or Cloudflare configuration?
You can get information about the evaluation of the technical infrastructure of your website by contacting Zeynart Web Bilişim.
Zeynart Web Informatics
Frequently asked questions
What approach is followed in the Worldwide PHP Security Alert process?
PHP, one of the most widely used programming languages in the internet world, came to the center of the technology agenda with serious security vulnerabilities that emerged in October 2026.
What is PHP2Shell? Why Is It So Important?
PHP2Shell is the name used to describe two critical vulnerabilities related to PHP's memory management. These vulnerabilities are tracked with the following security logs:
Cloudflare Takes Action: What does the Free Users Are Also Covered approach mean?
Cloudflare, one of the world's leading internet security and performance companies, announced the protection mechanisms it developed against PHP2Shell vulnerabilities to the public on October 21, 2026. According to Cloudflare's statement, security teams started working on protection rules before the vulnerabilities were announced to the public.
Every business is unique. Let’s explore how we can tailor these ideas to your own digital project.