
Security Issue Found in All Intel Processors
Unfortunately, there is no way to achieve anything done on a large scale perfectly. At some point, you're bound to have problems...
Unfortunately, there is no way to achieve anything done on a large scale perfectly. At some point, you're bound to have problems...
Unfortunately, there is no way to do anything done on a large scale perfectly. You're bound to run into problems at some point. this situation technology companies It is the same for and companies try to fix these issues using constant testing and feedback.
Intel's mobile, laptop and desktop products all processors An affecting problem has occurred. The problem described by Dutch researchers, especially older generation Intel processors also posed a threat. The name of the threat was determined as 'CrossTalk'.
What is CrossTalk?
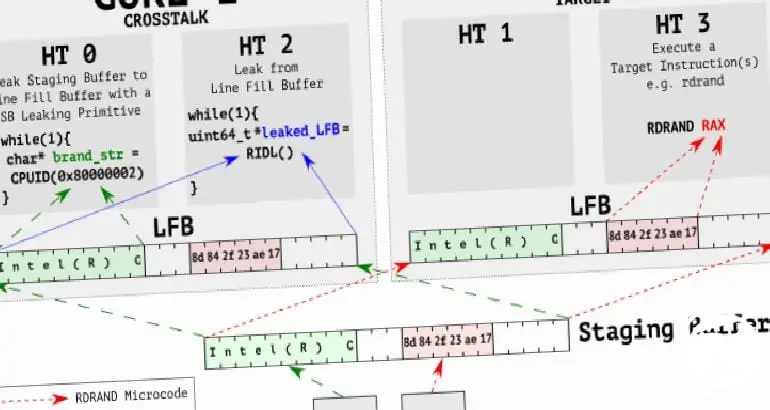
In its simplest terms CrossTalkWe can call it directing the processor cores to talk among themselves to leak information. In CrossTalk, one of the microarchitecture-scale data sampling attacks, attempts are made to obtain information while processing data in the processor.
Vrije University System and Network Security GroupIn the statement made by , these attacks Line Fill Buffer (LBF) It was stated that he collected the information revealed during the process. When we look at the details, we see that a data L.B.F. During the processing phase, leaks are obtained by examining the point at which an application is processed on different cores. This situation was even demonstrated with a video.
It took 21 months for the statement
Researchers this gap 21 months ago, says they reported it to Intel in September 2018. Normally, it takes 90 days for a vulnerability to be publicly disclosed. The reason for waiting so long this time was the complex structure of the deficit and the length of the necessary regulation process.
older Intel The company published a microcode for its processors. Released today and Special Register Buffer Data Sampling or SRBDS The code called (CVE-2020-0543, Intel-SA-00320) is available on the internet. If you are using one of the new processors, this may does not threaten. After the vulnerability emerged, Intel closed the vulnerabilities in its architecture that could cause this problem.

Zeynart Dijital Strateji & Yazılım Ekibi
Kıdemli Web Mimarisi, Yazılım & SEO Uzmanları
12+ yıllık kurumsal web tasarım, özel yazılım mimarisi, teknik SEO ve yüksek performanslı sunucu altyapısı deneyimiyle işletmeler için sürdürülebilir dijital çözümler üretir.
Every business is unique. Let’s explore how we can tailor these ideas to your own digital project.


Uzmanımıza Sorun & Yorumlar
Bu makaleyle ilgili merak ettiğiniz teknik detayları veya proje sorularınızı paylaşabilirsiniz. Yorumlar editör onayından sonra yayınlanır.