
Software Developer Working at Masomo Found Apple's Vulnerability Again
We had heard about Rıza Sabuncu, who works as a backend developer at Masomo, the developer of Head Ball 2, in the past months. A developer…
We had heard about Rıza Sabuncu, who works as a backend developer at Masomo, the developer of Head Ball 2, in the past months. A developer…
Working as a backend developer at Masomo, the developer of Head Ball 2 Rıza Sabuncu We heard about it in the past months. Rıza, who is also a bounty hunter as well as a developer, found a security vulnerability in the websites of the technology giant Apple and with $7,500 in money (approximately 59 thousand TL at today's exchange rate) was awarded.
During the past 4 months, Rıza Sabuncu continued his bounty hunt and yesterday a new success shared more. Rıza managed to receive an award by detecting a security vulnerability in Apple's internet services. Rıza, with the security vulnerability he reported to Apple in his post on Twitter. $2,500 prize He announced that he was the owner.
49 thousand lines of code, 15-20 days of work
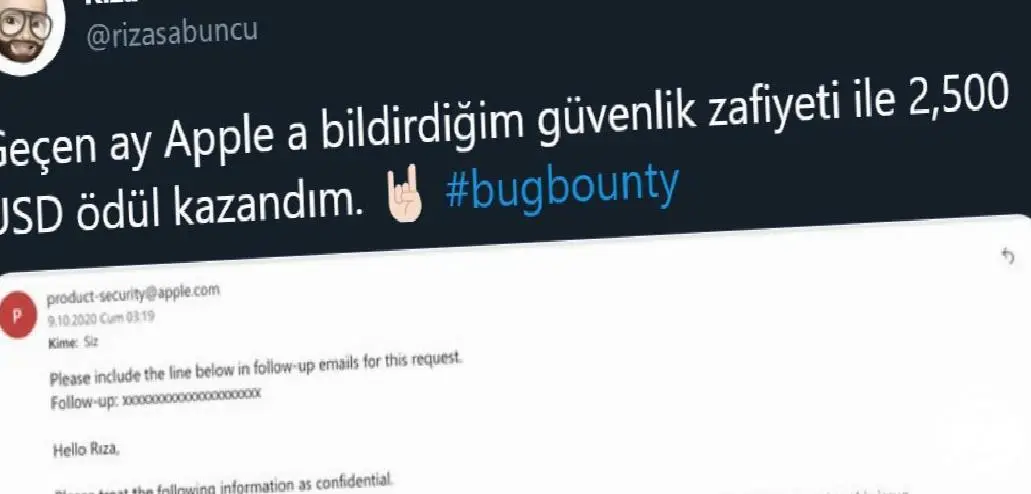
Naturally, Rıza Sabuncu cannot share detailed information about the security vulnerability he found in Apple. However, Rıza revealed the security vulnerability in his post last month. reported to Apple he stated. The status of the vulnerability during this time Apple Product Security It was reviewed by and the necessary reward was determined.
It can be seen in the Tweets that Rıza Sabuncu worked on the issue for a long time to find the security vulnerability. Because he used it to find security vulnerabilities in the answers he gave to his followers on Twitter. 49 thousand lines of code wrote, carried out 'directory fuzzing' on thousands of subdomains and a period of 15-20 days He shared that he discovered the vulnerability in it.
Rıza Sabuncu 2 times in the last 5 months Considering that he was rewarded by Apple, we seem to be hearing more about him in the coming months. Details of Rıza's success in the past months from the video below you can watch. To learn more about Apple Security Bounty, where Apple rewards those who find security vulnerabilities to this link You can click.

Zeynart Dijital Strateji & Yazılım Ekibi
Kıdemli Web Mimarisi, Yazılım & SEO Uzmanları
12+ yıllık kurumsal web tasarım, özel yazılım mimarisi, teknik SEO ve yüksek performanslı sunucu altyapısı deneyimiyle işletmeler için sürdürülebilir dijital çözümler üretir.
Every business is unique. Let’s explore how we can tailor these ideas to your own digital project.


Uzmanımıza Sorun & Yorumlar
Bu makaleyle ilgili merak ettiğiniz teknik detayları veya proje sorularınızı paylaşabilirsiniz. Yorumlar editör onayından sonra yayınlanır.